The Latest

The Malwarebytes connector for Claude checks suspicious links, phone numbers, and email addresses without leaving the chat. You can paste a link or upload a screenshot of a message, then ask Claude to check the details against Malwarebytes’ threat database. The connector works with free and paid Claude plans and requires no separate Malwarebytes account.

Setting permissions for each tool

The connector has six tools, including options to look up domain registration details, scan several items at once, and report suspected scams.

Malwarebytes Claude scam detection

You can set permissions for each tool separately. Ask requires Claude to request permission before each use. Always allow lets it use the tool without prompting. Block hides the tool from Claude.

Testing a connector

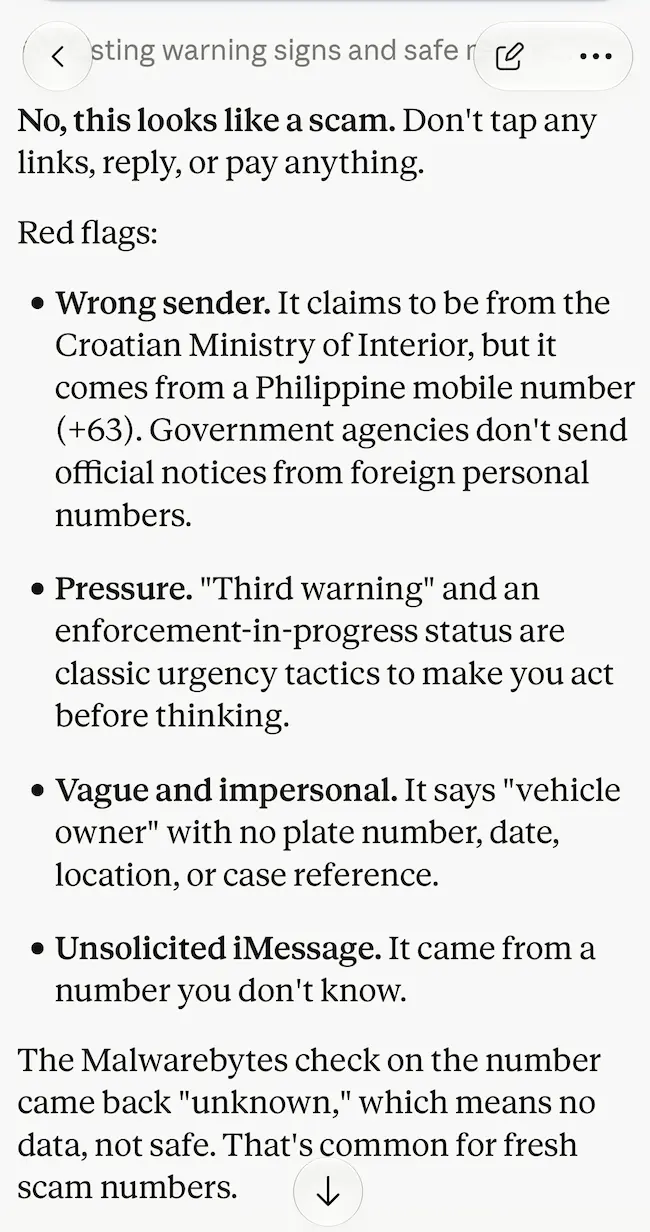
I tested the connector with two screenshots and left the tools set to Ask. The first showed a text claiming to come from Croatia’s Ministry of the Interior. It said I had an unpaid speeding fine and called itself a third warning. When Claude requested permission to check the sender’s number, I chose Allow once.

Malwarebytes Claude scam detection

Malwarebytes returned Unknown for the phone number. Claude flagged the message as a likely scam, citing the sender’s Philippine country code and the pressure to act.

Malwarebytes Claude scam detection

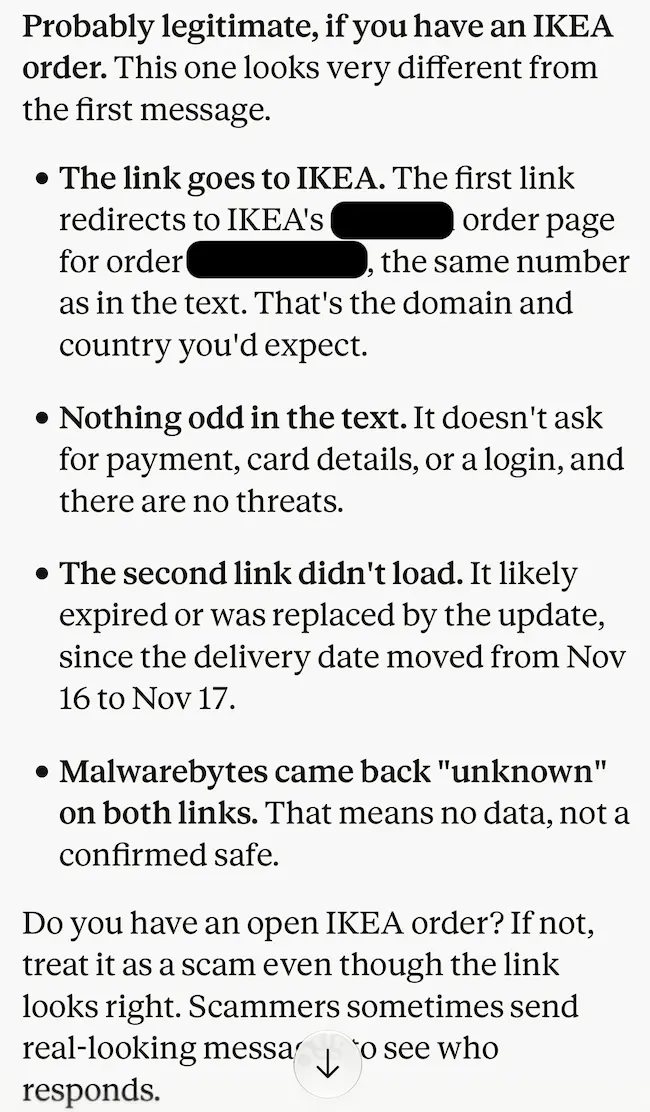
The second screenshot showed two IKEA delivery updates, each with a shortened link. Both came back Unknown. The scan showed that one link redirected toward an IKEA order page and marked the other Offline. Seeing the redirect gave me a detail to verify in the IKEA app without opening the link from the text.

Malwarebytes Claude scam detection

Conclusion

Malwarebytes and Claude helped identify signs of scam and explain why the message looked suspicious. The test showed how the integration can help you understand the risks before clicking a link or replying.


from Help Net Security https://ift.tt/m4hRMgw

Businesses looking to outsource cybersecurity want providers that can help them recover from attacks, manage AI risks, and explain what security problems mean for their operations, according to Barracuda What MSP Customers Need Next report.

MSP cybersecurity services

What MSP customers need next (Source: Barracuda Networks)

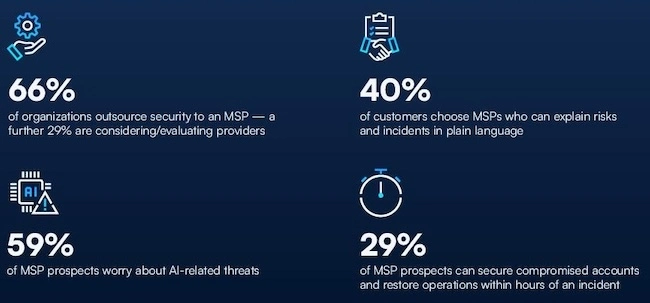
66% of surveyed organizations already outsource security services to a managed service provider (MSP), while another 29% are considering or evaluating providers.

Recovery remains a weak spot

Organizations considering an MSP are not reporting more security incidents than existing MSP customers. They report less confidence in their ability to detect threats, investigate incidents, and recover when an attack occurs.

“Organizations considering an MSP are not dealing with significantly more security incidents than existing MSP customers or organizations that manage security internally. The real difference is confidence,” Michelle Hodges, Senior Vice President, Global Channel and Alliances, Barracuda, explained.

Only 29% of prospective MSP customers said they could secure compromised accounts and restore operations within hours. Another 9% needed more than a week or could not do so consistently.

Of the organizations considering an MSP, 41% described their companywide security programs and policies as being at an early stage or only partially established. That figure reached 46% for maintaining a complete inventory of third parties with access to sensitive data.

AI adds to existing security concerns

AI-related threats worried 59% of organizations considering an MSP. Their concerns included phishing messages and social engineering generated with AI, unauthorized employee use of AI tools, and AI-enabled insider threats.

Customers also need help managing their own adoption of AI. That includes setting rules for its use and maintaining control of sensitive information handled through AI tools and workflows, Hodges wrote in an accompanying blog post.

Hiring more people was not the leading answer for prospective MSP customers. Only 23% said additional staff would have the greatest impact on security. Respondents placed greater emphasis on specialist expertise, better visibility into threats, AI-assisted investigation, and more time for prevention.

Plain language matters when choosing a provider

Some 95% of existing MSP customers said technical excellence mattered, while 40% identified plain-language explanations of risks, incidents, and next steps as a factor in choosing a provider.

Customers want providers who understand their industry and everyday operating pressures, and can explain security issues to business leaders who do not have a technical background.


from Help Net Security https://ift.tt/6C4vS0O

Attackers used stolen credentials to log in an average of eight minutes after infection across 27 confirmed infostealer cases, according to a report from Elastic Security Threat Command. Researchers also documented misuse of AI applications to execute commands and digitally signed remote monitoring tools to maintain access.

“An agent that holds credentials and can reach the internet is a new attack surface, whether it’s misconfigured or abused. When an attacker is behind it, its activity looks exactly like the employee who installed it. So the question for defenders isn’t whether a tool is approved; it’s what that tool is actually doing,” said Mike Nichols, General Manage, Security at Elastic.

Attackers run commands through AI applications

Coding assistants such as Claude Code and Cursor can execute system commands. Their ability to work with files, credentials, and other applications gives attackers ways to act through software installed for everyday work.

Researchers documented intrusions involving Claude Code on Windows and the ChatGPT desktop application on macOS.

In the Windows case, an attacker connected remotely to a computer and used Claude Code through its Visual Studio Code extension to prepare tools and reach an outside server through a concealed connection.

On macOS, commands run through the ChatGPT desktop application read an internal infrastructure document and then accessed the user’s saved password store.

These cases involved misuse after attackers obtained access. They do not establish that the applications contained a vulnerability or that their providers were compromised.

Stolen credentials used within minutes

Infostealers collect information such as saved passwords, browser session data, and payment details.

businesses remote access attacks

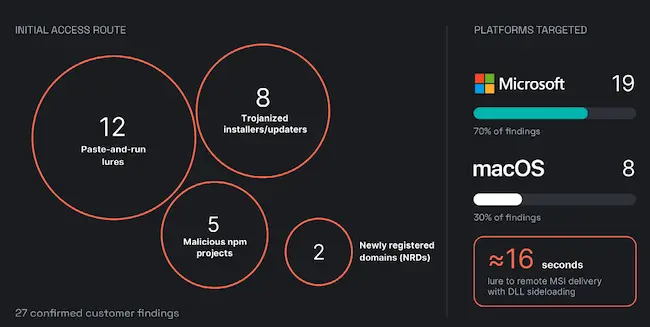
Confirmed infostealer findings by initial access route and platform (Source: Elastic)

Across 27 confirmed cases on customer computers, investigators observed theft operating through applications the user or operating system already trusted. These included a signed remote monitoring agent, a browser updater, a vendor installer, and Apple’s scripting utilities.

ClickFix-style verification pages were the most common entry point, appearing in 12 cases. These pages persuade people to copy and run a malicious command, often presented as a verification step or troubleshooting instruction.

The approach can bypass defenses focused on scanning email attachments because the user executes the command themselves.

In one healthcare case, delivery of a malicious installer and execution through DLL sideloading occurred about 16 seconds after the user followed the lure. DLL sideloading causes an application to load malicious code.

Captured session data can also allow attackers to use an account without entering its password again.

Remote IT tools provide continued access

Remote monitoring and management software lets IT staff connect to computers, transfer files, and run commands. Attackers can use those capabilities to control a device and deliver additional tools or malware.

Researchers confirmed 23 cases involving abuse of these applications. Phishing pages and archives containing malicious scripts led to installations, with ScreenConnect named most often.

One campaign began with a fake digital invitation and led to a hidden installation of ScreenConnect. The application connected to an attacker-controlled server and ran as a Windows service.

Another case involved an attacker uploading remote access software to a compromised server after attempts to create user accounts failed.

Phishing exploits trusted sign-in services

Attackers used trusted authentication services and preapproved applications to access cloud accounts.

Adversary-in-the-middle (AiTM) phishing kits place a relay between the victim and the real login page. When the victim enters credentials and completes multifactor authentication, the attacker can capture the resulting authenticated session.

Tycoon 2FA was one of the kits discussed and remained in active use during the reporting period.

Investigators observed attackers submitting stolen usernames and passwords through an older authentication method that allowed access without a second factor in those cases.

A separate device-code phishing case persuaded a user to enter a code on Microsoft’s sign-in page. The approval granted access to a session initiated by the attacker. Subsequent activity included registering a virtual device to support continued access.

“When attackers operate inside trusted software or on behalf of trusted users, the defensive answer is rarely just deploying a new signature. Detecting and neutralizing these threats requires user and entity behavior analytics (UEBA) to baseline normal activity, alongside cross-domain visibility and active correlation across your security environment,” the authors explained.


from Help Net Security https://ift.tt/Wl5OtHC

Here’s an overview of some of last week’s most interesting news, articles, interviews and videos:

Week in review

The first ten lines of a command policy for AI coding agents
In this Help Net Security interview, Vinay Thakker, CTO of KloudStax, explains how to set identity, credentials, and network limits for AI agents. He argues that agents should run under their own identity, with the person’s identity attached when acting on someone’s behalf.

Google disrupts XCPE botnet, bans the company behind it
Google shut down the servers behind XCPE, a backdoor hidden in the firmware of Android TV set-top boxes. Google’s Threat Intelligence Group attributes the operation with high confidence to Videostrong Technology, the company that manufactured many of those boxes. More than 1.3 million devices were enrolled.

Fireperf: Open-source network testing tool for firewalls and routers
The IPFire project has released fireperf, an open-source measurement tool that opens connections at a fixed rate and reports what the device in the middle did with each one. It is free software aimed at administrators, developers and testers who evaluate firewalls, routers and other systems that keep a state for every connection.

AI coding agents are installing MCP servers that will never be patched
When a developer tells an AI coding agent to “set up a GitHub MCP,” the agent has to pick a package. New research from Glow Labs documents sessions where it picked one out of an archived repository that will never be patched again.

What human hackers still do better than AI, according to HackerOne’s CEO
AI can find vulnerabilities in minutes, but people still hold the edge in judging what a flaw means for a business. In this Help Net Security interview, Kara Sprague, CEO of HackerOne, talks about business logic bugs, what AI does to the crowd model, and why routine medium-severity findings may pay less.

What AI-generated malware looks like under the microscope
In this Help Net Security interview, Lindsay Kaye, VP of Threat Intelligence at HUMAN Security, talks about what AI-generated malware looks like on the bench. She points to tidy comments, uniform logging messages, and emojis as signs a script came from a model, and notes that decompiled code strips much of that away.

AI agent detection signals that still work when agents look human
Bots follow a script. AI agents work toward a goal and choose their own steps, which makes them harder to catch. In this Help Net Security interview, Zohaib Ahmed, CEO of Resemble AI explains how agents arrive as declared, undeclared or disguised traffic, and why binary bot detection misses the last two groups.

A banking malware sample led researchers to an Android bug that can loop-crash phones
Bitdefender Labs researchers built an Android app that contains no executable code and requests no permissions, and installing it leaves a Pixel 10 in a crash loop that can take a factory reset to clear. The flaw, which Bitdefender calls GhostMap, comes from how Android reads the ZIP structure inside an APK.

Security certification is a snapshot, and buyers read too much into it
In this Help Net Security video, Mariia Bakhtina, a research specialist at Masaryk University, explains what a Common Criteria or FIPS-140 certificate does and does not promise. In her team’s analysis, about 6 in 10 vulnerabilities matched to certified products, smartcards aside, were disclosed after the certification date.

Chainalysis breached using “offensive agentic techniques”
Blockchain analytics firm Chainalysis has suffered a cybersecurity incident that led to a data breach. According to the company’s Friday announcement, the incident is unrelated to the recent Binance hack.

Second wave of refrigeration cyberattacks hits European supermarkets
Three weeks after the attack that turned refrigeration units in French supermarkets into ovens overnight, similar cyberattacks have hit shops in other European countries and again caused refrigerated food to be spoiled.

CISA to federal agencies: Remediate exploited Ivanti Connect Secure vulnerabilities (CVE-2026-111357, CVE-2026-118527)
CISA added two new Ivanti Connect Secure vulnerabilities (CVE-2026-111357, CVE-2026-118527) to its Known Exploited Vulnerabilities catalog on Friday, after Ivanti updated an earlier security advisory with details about the flaws.

AI agents scale and speed up Chinese-linked attacks
A China-nexus espionage group used AI agents to attack more than 200 organizations in 11 days, CrowdStrike said last week. On Monday, Kaspersky published details of a separate campaign against educational institutions in Africa and Latin America, mounted by Chinese-speaking operators.

Poisoned cPGuard update hits thousands of web hosting servers
An attacker has compromised the update infrastructure of cPGuard, a security suite for Linux web hosting servers, and pushed out a malicious update to nearly 3,000 customer servers. OPSShield, the company behind the security suite, also confirmed that the attacker made off with customer contact information and hashed passwords from the firm’s billing and licensing server.

Cyberattack hits French blood banks
Three blood banks have detected and reversed a potentially destructive temperature spike in their cold rooms, following a cyberattack that targeted a refrigeration equipment provider of the French Blood Establishment (EFS), the only civilian blood collection and transfusion organization in France.

Patched Zyxel GS1900 switches remained open to in-the-wild exploit (CVE-2026-107441)
Zyxel GS1900 series network switches that received a fix for a flaw that was later reported to have been exploited in the wild are still open to an exploit attackers used, Binarly found. That’s because the patch fixed a different bug (CVE-2026-7273) from the one (CVE-2026-107441) the exploit actually relies on.

Vercel ties login sessions to devices, rolls out AI security reviews in public beta
Vercel, the popular cloud platform for building and hosting websites and web applications, has announced the rollout of Device Bound Session Credentials (DBSC) and the launch of Vercel Security Review in public beta.

Product showcase: Sweet Virtual Patching stops HTTP2Shell while fixes catch up
Sweet Security helps teams identify exposed services at runtime, and its Virtual Patching blocks the system call the demonstrated exploit uses to launch a shell, buying time to deploy permanent fixes.

Opal’s agent.ID virtual event: Top security leaders on governing Al agents
Opal Security hosted agent.ID, a free virtual event focused on adapting identity and access management (IAM) to AI agents, on November 5, 2026. The event brought together CISOs and identity leaders from Elastic, Instacart, Notion, Databricks, Knostic and other organizations to discuss how agents could be governed through assigned ownership, defined permissions and accountability.

Novee puts forgotten internet-facing assets through penetration testing
Novee’s External Surface Testing is a new capability in its AI penetration testing platform that helps security teams discover internet-facing assets and validate exploitable vulnerabilities. It tests newly disclosed CVEs and findings imported from third-party external attack surface management (EASM) tools.

Secure your containers without breaking what works
Container security has a familiar problem. Teams identify vulnerabilities, but turning those findings into lower risk is much harder. A standard container image may include operating-system packages, development tools, debugging utilities and libraries that an application never uses. Each unnecessary component can expand the attack surface and add vulnerabilities to investigate, patch or explain during an audit.

Live Q&A: CISSP exam prep with ISC2 experts
ISC2 hosted a live Q&A about the CISSP exam on November 6, 2026, at 7:00 p.m. CET. Experts answered questions, explained certification requirements, reviewed the exam domains, and shared self-study resources and training options.

November 2026 Patch Tuesday forecast: Old software continues to bite
Still working through October’s Patch Tuesday updates, or ready for another round next week? Microsoft fixed a record-breaking 1,400-plus vulnerabilities, including CVE-2026-96951, an actively exploited Windows Shell flaw that bypasses Mark of the Web protections. October also brought PHP2Shell: two critical PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, that could allow unauthenticated attackers to execute code on web servers. Emergency patches are available.

Ransomware gang talked AI agents into doing much of its dirty work
The group behind the Aur0ra ransomware has been using AI agents to move through victim networks, collect credentials and work its way up to domain administrator access, according to Sophos.

FBI pins $6.3 billion Binance crypto heist on North Korea while scammers circle anxious users
North Korea was behind the theft of more than $6 billion in cryptocurrency from Binance, the FBI has confirmed. The agency tied the attack to TraderTraitor, the North Korean group it named in the $1.5 billion Bybit hack of February 2025. Blockchain intelligence firms TRM Labs and Chainalysis were the first to attribute the heist to the group, within a day of the attack.

AI-powered infostealer picks out the most profitable parts of your stolen data
A new Windows infostealer sends the data it steals to an AI model and asks it to rank the victim’s assets by how much money they could bring in, Cisco Talos has found.

Stolen AI access leaves companies with cloud bills of up to $1 million
Criminals who break into corporate cloud accounts are using the stolen access to run AI models at the victim’s expense, in some cases racking up more than $100,000 in charges in a single day, Google Threat Intelligence Group (GTIG) and Mandiant researchers have found.

Attackers exploit critical Node-RED flaw to deploy Linux bot and backdoors (CVE-2026-58115)
Attackers are exploiting an authentication flaw (CVE-2026-58115) in Node-RED, a programming tool built into some industrial control products, to install a Linux bot and backdoors on unprotected servers, VulnCheck has found.

Police seize over 100 servers linked to investment fraud with more than €4 million in losses
Seven people have been arrested and more than 100 servers seized in a coordinated law enforcement action against an investment fraud network that started unravelling after a complaint from a German couple.

Fake job interview opened the door to $6.34 billion Binance heist
A tampered software installer and a fake job interview gave attackers the access they needed to steal about $6.34 billion in digital assets from Binance. The money left Binance wallets on October 29, in what is likely the biggest crypto heist in the history. Tether, Circle and other partners helped freeze close to $3 billion of the stolen funds within the first day, and the exchange promised to cover all user losses.

Russian hackers target iOS and Android users with n-day exploits
Russia’s APT29 has been using compromised websites, lookalike domains and a hijacked web analytics service to target iOS and Android users with exploits for patched flaws and steal their cookies, messages and Wi-Fi passwords, according to Sekoia.

OpenAI’s upcoming AI model built 948 working Linux root exploits in a single run
An automated system running on an upcoming AI model turned hundreds of Linux kernel bugs into working exploits that give an ordinary user root access, and wrote a patch for each underlying flaw, OpenAI revealed in a new research post.

Scammers capitalize on GTA 6 hype to push malware and crypto cons
Scammers are offering supposed leaked builds, early copies and phone versions of Grand Theft Auto VI (GTA 6) weeks before the game’s November 19 launch, Netcraft warned in a new blog post.

Cyberattack on Norway’s aid agency may have swept up all user data
The names and email addresses of 20,614 people registered on Norad’s Grants Portal may have ended up in the hands of attackers, Norway’s development aid agency has disclosed.

Rental phishing sites use live chat to win over hesitant travelers
Holiday travelers looking for a place to stay are landing on copies of popular rental platforms, complete with host names, ratings and reviews, that ask for their passwords, personal details and credit card numbers. The sites, spotted and taken down by Fortra’s Intelligence and Research Experts (FIRE) team, rely on familiar branding, copied property listings and reservation details, along with urgent messages meant to rush visitors into acting.

Residential proxy traffic caught leaving the White House network
The White House network has been working as an exit point for residential proxy services, a setup that may open a path into one of the most closely guarded networks in the world, Layer3 Intel found.

OpenSSH flaw exploited in the wild just hours after disclosure (CVE-2026-123158)
An OpenSSH flaw that lets remote attackers log into passwordless accounts on Alpine Linux and other musl-based systems is being exploited, threat intelligence firm Previdian has warned.

US agencies warn attackers are targeting refrigeration systems that protect food and medicine
Threat actors are going after the controllers that keep grocery store freezers and cold storage rooms at safe temperatures, and they may push those units into continuous heating and defrost cycles, five US federal agencies warned in a joint advisory published on Thursday.

Product showcase: Trust Onion uses rotating codewords to verify callers
Trust Onion is a free app that gives trusted groups three rotating codewords to check who they are communicating with. It also includes signed selfies, message checks, and callback requests. It is available for macOS, iOS, and Android.

Byoky: Open-source wallet for AI API keys
Byoky is an open-source wallet for AI API keys, available as a Chrome and Firefox extension and as iOS and Android apps. Users store their keys for OpenAI, Anthropic, Google Gemini and other providers in it, encrypted on their own device.

DeepSeek open-sources Super-Agent, a coding agent that watches team chats for work
Deepseek released a research prototype of dsh-superagent, a coding agent that does work on a GitHub repository for you. The agent gets to work in two situations: an allowed user asks for something, or a rule your team wrote covers it. You can also open up a chat or GitHub scope, and then anyone in it can request work just by mentioning the agent.

OpenAI raises top bug bounty payout to $172,000 with bonuses
OpenAI increased its security bug bounties to encourage independent researchers to find vulnerabilities in its software. The program now offers bonuses for high-quality reports.

Gorbag APT group hits Ukrainian courts and city councils with self-deleting malware
ESET has been tracking a Russia-aligned group it calls Gorbag, which has been breaking into Ukrainian organizations since at least February 2025 using spearphishing attachments and a stealer that erases itself once the data is gone.

Anthropic open-sources FlashProve, its provable inference prototype for MoE models
Anthropic’s Frontier Red Team, with collaborators at EPFL, MIT and StarkWare, built FlashProve, a prototype that produces a cryptographic proof that one specific language model generated one specific reply. The prover, two verifiers, the formal proofs behind them and a protocol specification are on GitHub under the Apache 2.0 license.

NIST publishes cybersecurity guide for businesses too small to have IT staff
The National Institute of Standards and Technology (NIST) released cybersecurity guidance for small businesses with no paid employees other than their owners. These businesses include freelancers, sole proprietors, and independent contractors.

Companies going all in on AI could see their strategy backfire
Four of the five highest-ranked enterprise risks in Gartner’s Quarterly Emerging Risk Report were AI-related. AI strategy miscalculation and AI-driven competitive displacement debuted at No. 3 and No. 4, respectively. The AI workforce preparedness gap held fifth place.

Ghostunnel: Open-source TLS proxy with mutual authentication
Ghostunnel is an open-source proxy that handles TLS for programs that cannot handle it themselves. It works in two directions. In server mode it sits in front of a backend, accepts TLS connections, checks the client’s certificate, then passes traffic to the service behind it over TCP or a UNIX socket. In client mode it does the reverse, listening for plain local connections, wrapping them in TLS and presenting a client certificate to the remote service.

Open-source file sync tool rsync 3.5.2 fixes a CPU exhaustion flaw
The rsync project released version 3.5.2, and it closes a flaw that let a connecting client tie up a server’s CPU with checksum math that leads nowhere. The new version also lets you push a transfer to the back of the queue for CPU and disk, so a big sync stops elbowing everything else on the machine.

Most consumers aren’t ready to let AI agents shop unsupervised
Customer control, account security and ease of use are influencing the adoption of AI agents that make purchases, book services and access personal information, according to Okta’s 2026 Customer Identity Trends Report.

Companies are spending more on AI governance and getting less control
Companies are increasing their cybersecurity budgets, with AI security and governance the top priority for additional spending, followed by cloud security, according to DNSFilter’s The Cost of Shadow AI report.

Healthcare can’t govern the AI tools it hasn’t found yet
Nearly nine in ten healthcare leaders say security or compliance staff always or usually review AI-written code that touches patient data before it goes live, and seven in ten have still found an AI-built tool handling that data without IT or security knowing, according to Paubox.

Apple is bringing harmful content checks to iCloud link sharing with potential account penalties
Apple will begin checking iCloud content shared using the “Anyone with the link” option for harmful material in iOS, iPadOS, macOS, and visionOS 27.3 or later. When sharing content stored in iCloud, users can choose “Share a Link” or “Send a Copy.” Those who choose “Share a Link” can restrict access to people they invite or approve, or allow anyone with the link to access the content.

Google puts new limits on AI agents that hunt threats and fix vulnerabilities
Google Cloud is adding new controls to CodeMender, its AI tool for finding and fixing software vulnerabilities, allowing businesses to isolate attack simulations and target code scans more precisely.

99% of repository access tokens never expire
Developers, automated tools and AI coding agents hold permissions that can outlast the work they were granted for. Without access reviews, organizations can leave accounts able to copy or change company code after the work ends, according to BlueFlag Security’s The State of Developer Risk 2026 report.

87% say their AI controls need to work better
The AI running inside large companies has stopped waiting for permission. Across five categories of AI, from chatbots to process automation, more than half of 3,600 business decision-makers say the systems their teams use can act within defined rules without routine review, or finish whole processes with no human approval.

OpenAI’s GPT-6 Cyber found 81 Firefox flaws earlier AI testing missed
OpenAI has introduced GPT-6 Cyber, a version of GPT-6 Astra trained to find software vulnerabilities, test how attackers could exploit them, and help develop fixes. The model is designed for authorized security testing of websites and applications.

Cybersecurity jobs available right now: November 3, 2026
We’ve scoured the market to bring you a selection of roles that span various skill levels within the cybersecurity field. Check out this weekly selection of cybersecurity jobs available right now.

from Help Net Security https://ift.tt/l40CTL1

We may earn a commission from links on this page. Deal pricing and availability subject to change after time of publication.

If you’re browsing home security options, Ring has one of the best early Black Friday deals that should be on your radar. Right now, you can add an indoor camera and another one at your front door for less than $65. The Ring Indoor Cam 2K is 58% off at $24.99 (originally $59.99), while the Ring Battery Doorbell 2K is 60% off at $39.99 (originally $99.99)—both at their lowest-ever price.

Both offer features like 2K video and two-way talk, but the indoor cam is the simpler purchase if you mainly want to check on a pet or kids and see what’s happening near an entrance. It plugs into an outlet, so there’s no battery to recharge, and its low-light color video helps preserve detail when lights are off or dimmed. However, since it’s a fixed-view camera, keep in mind that you’ll need to position it carefully.

It also has a removable lens cover to block the camera’s view, which is a nice privacy perk, though closing the cover doesn’t turn off the microphone. For complete audio privacy, you need to disable the microphone in the Ring app.

The Battery Doorbell is the better pick if alerting you to visitors, deliveries, and potential intruders is your priority. It has a 140-degree horizontal and vertical field of view that provides head-to-toe framing, plus up to 6x zoom for better detail. You can install it without wiring, though you’ll need to recharge its built-in battery. It also requires a 2.4GHz wifi network.

The main catch with both devices is the ongoing subscription cost: Live viewing, two-way talk, and basic real-time notifications all work without a subscription, but reviewing saved footage requires a paid plan, starting at $4.99 per month or $49.99 annually for one device; coverage for multiple devices at one location starts at $9.99 monthly or $99.99 annually.

At these prices, the Ring Indoor Cam 2K is perfect for occasional live check-ins, while the Ring Battery Doorbell 2K is better suited to monitoring your front entrance. Buying both makes sense if you already have a Ring plan that covers extra devices.

Our Best Editor-Vetted Early Black Friday Deals Right Now
Deals are selected by our commerce team

from Lifehacker https://ift.tt/0R1v5fd

We may earn a commission from links on this page.

If you've spent any time in or around running culture over the last few years, you've undoubtedly encountered someone preaching the gospel of Zone 2 cardio. Legend has it that easy, conversational effort cardio—also known as cardio that takes your heart rate into "Zone 2"—is the secret to unlocking everything from a bigger aerobic engine to faster race times and even a longer life.

To train by heart rate, you aim to keep your heart rate in the "zone" that gives you the desired workout. The catch is that Zone 2 is easy to get wrong, especially since no one can agree on what it actually means.  Your smartwatch can show you your heart rate, but many recreational runners will still drift into a “gray zone” that's too fast to be truly easy, and too slow to give them a real workout. If you're struggling to hit Zone 2 consistently, there are a few smartwatch hacks that can help.

Swap pace for heart rate as your primary data field to account for day-to-day variables

Pace can be a distraction during easy runs, especially considering all the different variables that affect your effort, like hills, humidity, and general fatigue. A 9:30 mile might be Zone 2 on a flat, cool day and Zone 4 on a hot, hilly one.

Dig into your watch's activity settings (on Garmin, it's Activity > Data Screens; on Apple Watch, the Workout app's metrics layout; on Coros, Polar, and Suunto, similar menus) and put live heart rate zone front and center, ideally as a zone number or colored gauge rather than just a raw bpm figure (though this assumes these zones are accurate—more on that below).

Set audio and haptic alerts for your zone ceilings to know when you're leaving your zone

Create an alert when your heart rate goes above or below a target range, delivered as a vibration pattern, a beep, or both. Set the alert for the upper boundary of Zone 2, and you've essentially hired a mini coach who taps you on the wrist whenever you get overzealous. Whenever you hear or feel that buzz, you’ll know you need to ease into a slower jog until your heart rate settles.

Build custom workouts with target ranges so you hit your zone targets every time

Instead of free-running and checking your numbers afterward, build structured workouts that carry the targets for you. In Garmin Connect, TrainingPeaks, Apple's Custom Workout feature, Coros Training Hub, or similar platforms, you can create sessions like "10-minute warm-up in Zone 1, 40 minutes in Zone 2, 5-minute cooldown" and sync them straight to your watch.

During the run, your watch displays the current step, the target range, and whether you're above, below, or in the pocket. Many will automatically advance between intervals and alert you when it's time to shift gears.

This is especially powerful for:

  • Heart rate-based intervals, like 4 x 4 minutes in Zone 4 with Zone 1 recovery, where you don't have to do mental math or check the clock.

  • Progressive long runs that start in Zone 2 and finish in Zone 3.

  • Hill repeats, where pace is meaningless but effort matters.

Set your zones properly (i.e., don't trust your watch's defaults)

Most watches calculate default zones using a generic formula like 220 minus your age, which can be off by 10 to 20 beats for any given individual. If your zones are wrong, your Zone 2 training isn't Zone 2 training.

Here’s how to fix your watch’s heart rate zones:

  • Find your true max heart rate. The informal way is to just notice what number you see on your watch when you can no longer speak comfortably; the more formal way is this treadmill test. You can also look through your recent hard efforts, like races, hill repeats, or all-out intervals, and see the highest sustained heart rate you've recorded.

  • Use lactate threshold heart rate instead. Many watches can estimate this automatically after a few hard efforts, and zones built from threshold tend to be more personalized than ones built from max.

  • Customize the boundaries. Dive into the heart rate zone settings and input your own numbers. Some runners prefer the "MAF" method (180 minus age, with adjustments) for aerobic base building, and most watches let you set that as a custom range.

  • Recheck every few months. Fitness changes, and so do your zones.

Strip away distracting data screens to help you stay in the zone

A screen crowded with cadence, vertical oscillation, ground contact time, running power, and lap pace is a recipe for second-guessing.

Create a dedicated Zone 2 data screen with just two or three fields: current heart rate zone, elapsed time, and maybe distance. Turn off auto-scroll so it doesn't flip to a screen full of numbers you don't need. If your watch supports multiple activity profiles, make a separate "Easy Run" profile with this stripped-down layout and keep a different profile for tempo days and races.

Bonus tip: Use a chest strap for more accurate heart rate readings

A chest strap (or a forearm or upper-arm optical band) is generally more accurate and responsive than the wrist-based sensor on your watch. For heart rate training, where a few beats can mean the difference between Zone 2 and Zone 3, I recommend buying one. This COOSPO heart rate monitor is one of my favorites, and it's only $31.99.

The bottom line: Your smartwatch can make heart rate training far easier, but only if you set it up to support you rather than overwhelm you.


from Lifehacker https://ift.tt/WweUu8y

We may earn a commission from links on this page.

Following the dramatic conclusion of Cyberpunk: Edgerunners way back in 2022, the show has returned for a new season set in the megalopolis of Night City with a standalone story and a new cast of characters (by necessity).

Though the aesthetic and themes of cyberpunk have their roots in American science fiction of the 1970s and '80s, anime and manga of the '90s and beyond embraced the form and took it to entirely new places—so much so that a Japanese/Polish co-production of an adaptation of a video game from a Polish designer has taken its cues from a couple of decades' worth of great anime and cerebral sci-fi. Which is to say, if you're looking for more heady sci-fi series, these 10 are a good place to start.

Cowboy Bebop (1998 – 1999)

An iconic, effortlessly cool genre classic, Cowboy Bebop is one of the undisputed GOATs of anime, blending western, noir, and crime genres and setting the resultant mash to a killer soundtrack of old-school jazz (which serves much the same purpose as Cyberpunk's propulsive electronic grooves). The title's "cowboys" are bounty hunters in a near-future in which humans have been forced to colonize the solar system after Earth became uninhabitable. Different settings, but both shows offer up ragtag crews with highly dubious fates. Former hitman Spike Spiegel leads his crew on one nearly disastrous mission after another, their standalone adventures all building to a thoroughly memorable climax. Stream Cowboy Bebop on Crunchyroll or buy it from Prime Video.


Psycho-Pass (2012 – 2019)

This one's set in 22nd-century Japan, with a slick Blade Runner-esque aesthetic and a setup reminiscent of Minority Report. Here, technology exists to measure intentions, so crimes can be stopped before they’ve occurred, at which point the “criminals” are placed into psychological treatment (à la A Clockwork Orange)—or subject to summary execution because their threat potential is too high. That ability to predict behavior bleeds over into every aspect of life: careers and even relationships are determined in large part by the same systems that sniff out criminal intent. Obviously, this is all perfectly fine, and there’s no potential for abuse or miscalculation whatsoever...though there are a couple of warning signs. The first involves a new Enforcer who becomes a potential murderer himself when he miscalculates the extent of a criminal’s potential to do wrong, and, even more significantly, the existence of a criminal mastermind who is somehow invisible to the tech, even as his criminal actions grow more and more elaborate. Stream Psycho-Pass on Prime Video and Crunchyroll.


Love, Death & Robots (2019 – 2025)

Created by Tim Miller and with director David Fincher as an executive producer, this animated anthology series is a grab bag of wildly diverse offerings: Each episode is produced by a different international studio, with the only link between them being one of the three words in the show's title. One episode deals with robotic gladiator fights in dystopian London, another finds us under the threat of sentient yogurt, yet another finds an ambitious cat learning to make use of a family's robot helper. Its format dictates that no two episodes are going to have the same premise, but it shares with Cyberpunk an edgy sensibility and stories set in an apocalyptic future, albeit with a dark sense of humor—its four seasons offer up a mix of tech, sex, violence, and gorgeous animation. Stream Love, Death & Robots on Netflix.


Ghost in the Shell: Stand Alone Complex (2002 – 2005)

One of several completely standalone spinoffs of the wildly influential 1995 film (itself based on the beloved manga series), Stand Alone Complex requires no prior knowledge. The style is largely the draw, as the series luxuriates in its fictional Nihama City setting, a world unto itself in a future Japan in which cybernetic people hack directly into the internet. Our sympathies are more with the authorities—in this case, Public Security Section 9, a cybercrime and antiterrorism police unit—than the cyber criminals, but the show approaches some of the same themes as Edgerunners with legit punk style. Stream Ghost in the Shell: Stand Alone Complex on Tubi and The Criterion Channel.


Altered Carbon (2018 – 2020)

In this adaptation of the Richard K. Morgan cyberpunk classic of the same name, Joel Kinnaman and Anthony Mackie (yes, both of them) star as Takeshi "Tak" Kovacs. In this future megacity setting, human consciousness can be transferred between bodies. The tech is widely available, but only the wealthy can afford the backups and protections that make it a form of virtual immortality. Kovacs is a former soldier turned mercenary, revived from a backup after 200 years by Laurens Bancroft (James Purefoy), one of the wealthiest men alive. His motives for bringing the man back are shrouded in mystery, but he's giving Tak a chance to solve a very cold case: his own murder. Stream Altered Carbon on Netflix.


Arcane (2021 – 2024)

Another popular (and Emmy-winning) game adaptation, Arcane is based on League of Legends, a top-down actioner involving online opponents shooting lasers across a map. It doesn't sound like fodder for a show this impressive, but here we are. The League of Legends lore forms the backdrop for the show, but the pull is in the narrative involving two sisters caught up in the growing conflict between a utopian city and its oppressed underclass, without whom it couldn’t exist. The painted animation style is truly something special—not a stylistic match for Cyberpunk, but the two shows both go far above and beyond to create striking visual worlds. Stream Arcane on Netflix.


Trigun (1998)

Vash the Stampede is a hunted outcast with a dark history that slowly comes to light over the course of the series. He’s got a reputation as a human wrecking ball, bringing destruction wherever he goes, and seemingly just for fun—but in reality he’s far more respectful of life than his pursuers. Still, cities evacuate at the mere possibility of his arrival, and a huge bounty sits on his head (no matter that the bounty hunters do far more damage than Vash). He and his friends—actually a couple of insurance agents—find themselves in a series of misadventures on the planet Gunsmoke, building to a final showdown that caps the series with finality. Visually, it’s probably one of the defining ‘90s shōnen-style action series, with elegantly choreographed gunfights that never get old. Tonally similar, Trigun also shares with Cyberpunk 2 the work of legendary composer Tsuneo Imahori, his music being crucial to both shows. Stream Trigun on Crunchyroll or buy it from Prime Video.


Darling in the Franxx (2018)

Another from animation studio Trigger, Darling in the Franxx leans heavily into the mecha sub-genre, set in a post-apocalypse where children are bred and indoctrinated into piloting the title's massive Franxx to defend the remnants of humanity. Adults are pretty much immortal, so the kids simply don't have any other utility. Two of these teens begin to develop romantic feelings for each other, potentially complicating their usefulness to society and leading to an explosive, bittersweet finale. Stream Darling in the Franxx on Crunchyroll or buy it from Prime Video.


Killjoys (2015 – 2019)

What starts out as a relatively straightforward action show about space bounty hunters (the title's “Killjoys”) develops surprising depth over the course of its five seasons. As officially sanctioned Killjoys, the trio at the show’s heart (Hannah John-Kamen, Aaron Ashmore, and Luke Macfarlane) are bound to remain politically neutral at any cost. Initially, that’s a way to get them right into the heat of a fight, but as they develop ties of friendship and family in an exploited community, they come to understand the high cost of unchecked wealth and greed, and the ways in which neutrality always benefits the oppressors. The show’s creators make exceptionally good use of a limited budget and offer up some impressive queer rep along the way, a rarity in pop sci-fi. Stream Killjoys on Tubi or buy it from Prime Video and Apple TV.


Akudama Drive (2020)

Another great cyberpunk metropolis: here it's Kansai, an increasingly lawless city run by elite criminals known as Akudama. An ordinary girl, quite inadvertently, becomes caught up in a major planned heist and is forced to fake credentials as a master swindler in order to stay alive. Like Cyberpunk, the show tackles anti-authoritarian themes among a diverse crew of outsiders. Stream Akudama Drive on Cunrchyroll or buy it from Prime Video.


from Lifehacker https://ift.tt/YsWDK0a