The Latest

We may earn a commission from links on this page. Deal pricing and availability subject to change after time of publication.

There's a reason the MacBook Pro is so expensive. Apple saves its most premium features for this product line—mini-LED displays, built-in fans, HDMI and SD ports, and, depending on the model, the most powerful chips. None of these comes cheap, and, after recent RAM-related price hikes, the MacBook Pro now starts at a steep $1,999. That's not the case during October Prime Day, however: Right now, you can take a decent chunk off many MacBook Pro models, and even more if you opt for one of Apple's M5 Pro or M5 Pro Max devices.

You can save $160 on the M5 MacBook Pro

Let's start with the standard M5 MacBook Pro. This uses a similar M5 chip to the one found in the MacBook Air, though the Pro does come with 10 GPU cores (that costs extra on the Air). Other than that, these are the same processors, running the same 16GB of RAM—though the M5 MacBook Pro comes with 1TB of storage standard. You also get most of the hardware perks of the other MacBook Pro devices, without venturing into $2,499 and up territory, including three USB-C ports, the HDMI and SD card ports, a 14.2-inch mini-LED display, and a 12MP FaceTime camera. Typically, that'd cost you $1,999. But on Amazon, you can pick this machine up today for $1,869.

Save $155 on the 14-inch M5 Pro MacBook Pro

This is a great price for this MacBook, but it's not the only savings you'll find on MacBook Pros this October Prime Day. If you upgrade to the M5 Pro MacBook Pro, you can save $155 off its retail price, bringing the machine down to $2,345 from $2,499. With this laptop, you get all the perks of the M5 MacBook Pro, but with the M5 Pro chip, which is much more powerful. This chip comes with a 15-core CPU and 16-core GPU, along with 24GB of RAM and a 1TB SSD. It also supports Wi-Fi 7, while the M5 MacBook Pro only supports Wi-Fi 6E.

Amazon also has the M5 Pro MacBook Pro with an 18-core CPU and 20-core GPU $150 off. But the biggest discounts are on Apple's most expensive 14-inch MacBook Pros. If you're in the market for a souped-up M5 Pro model, or one of Apple's M5 Max configurations, Amazon has huge discounts:

Save $150 on the 16-inch M5 Pro MacBook Pro

Similarly, Amazon has big discounts on the 16-inch version of these MacBook Pros. The best option for most people in this category is going to be the base model 16-inch, which comes with the M5 Pro with an 18-core CPU and 20-core GPU, as well as 24GB of RAM and a 1TB SSD.

But as with the 14-inch MacBook Pros, the biggest deals are on the most expensive 16-inch Pros. Here's how much you can save:

October Prime Day FAQ

When is Prime Day in October?

Amazon Prime Day is an annual event held in June or July. Amazon's October Prime Day event, known as Prime Big Deal Days, is a two-day sale that starts Oct. 6 and ends on Oct. 7.

What goes on sale during October Prime Day?

Since Prime Big Deal Days happens in the fall, you're likely to see more deals on gaming and indoor gym equipment. Amazon has already announced some of the 35 categories that will be on sale, including beauty, tech, kitchen, fashion, and home. Some brands Amazon has already mentioned are: Shark, Princess Polly, Soundcore by Anker, UGG, Nest New York, Sony, Tarte, Adidas, and Barefoot Dreams.

Is Prime Day once a year?

Prime Day happens every summer. Prime Big Deal Days (or October Prime Day) happens every October. Amazon's Big Spring Sale happens every spring.

Our Best Editor-Vetted Prime Day Deals Right Now
Deals are selected by our commerce team

from Lifehacker https://ift.tt/c5UMxSi

We may earn a commission from links on this page.

A new Google wearable may be on the way, and leaked pictures suggest it may be a fitness band with a screen, a successor to the Fitbit Charge 6. Android Headlines reports that the new device will be called the Fitbit Edge. 

Earlier this year, Google ran ads on Reddit that seemed to show a new fitness band alongside Pixel watches and phones. In a post titled “Um so what the hell is that??,” redditors debated whether the unfamiliar wearable was an accidental leak of a yet-unreleased device, or just an AI hallucination. After all, if you asked an AI to create a hybrid of a Fitbit and a Pixel Watch, it would look more or less like what was in the picture.

What rumors say about the new "Fitbit Edge"

The leaked photos appearing at Android Headlines look like the device from the ad. It has an oval screen, only about as wide as the wristband and taller than it is wide. The rounded edges and the style of watch band match aesthetically with Pixel Watches, while the overall form factor—a tall screen set into a thin wristband—fits the design of the old Fitbit Charge 6. 

According to spec sheets that were reportedly also included in the leak, the device will have GPS, an altimeter, and a seven-day battery life. That's the same battery life as the Charge 6, which had GPS but no altimeter. The new device is said to work with both iOS and Android, as the Fitbit Air does, rather than being Android-only like the Pixel Watch. The rumors do not include a price, a release date, or a full list of features.

What this means, if true

If it weren’t for the earlier ad—the one that many thought was a hallucination—I probably wouldn’t have expected Google to release a device like this at all. Its last fitness tracker with a screen was the Fitbit Charge 6 in 2023. The Fitbit Air makes sense since smart bands are having a moment, and the Fitbit Air is a really well-executed one. But I wasn’t sure if Google was interested in continuing the Fitbit line beyond that one device. 

It’s a good idea, I think. Small trackers are easy to wear (and forget you’re wearing), but sometimes you just want to be able to see the time on your wrist. If Google is smart, they’ll allow you to swap seamlessly between the new device and the screenless Fitbit Air. (Currently, you can pair one Pixel Watch and one Fitbit to your phone, but you can’t pair two different models of Fitbit.) 

I’m excited to see what Google has in mind for the new device, assuming the rumors are true about its size, shape, and capabilities. I was disappointed by all the things the Charge 6 couldn’t do, and I hope the new Fitbit doesn’t repeat those mistakes. For example, the Charge 6 can control the music that’s playing on your phone, but only if you pay for a YouTube Music subscription. Most fitness watches—including Garmin, Coros, and Suunto watches I’ve tried—will simply give you controls for whatever is playing on your phone, no matter what app it comes from. 

If it’s true that the new device also has its own GPS and altimeter, that’s also exciting—but I’m skeptical that Google will be able to stuff in high-quality versions of those components in the space available. The Charge 6, I found, had trouble getting a good GPS reading and a good heart rate reading at the same time. But the Fitbit Air is surprisingly small and capable for its size, so I’m looking forward to seeing what the new device might be able to do.


from Lifehacker https://ift.tt/Batq7jS

We may earn a commission from links on this page. Deal pricing and availability subject to change after time of publication.

The October Prime Day sale is officially here, and the best deals on headphones, fitness tech, and other essentials from premium brands are popping up all over Amazon. Right now, these Sony LinkBuds Clip Open Earbuds are down to $158 (originally $229.99), an all-time low according to price tracking tools.

One of the top Prime Day earbuds deals for people who dislike conventional in-ear buds, the Sony LinkBuds Clip gets praise in PCMag for crystal-clear audio and long-lasting battery life. With a lightweight clip-on design that sits outside the ear canal and lets you hear background noise like traffic or announcements, they’re a useful essential for errand runs, busy workdays, dog walks, and other settings where you don’t want total noise cancellation. An IPX4 rating can handle sweat and light rain, while multipoint pairing lets you stay connected to devices without constant re-pairing. 

The earbuds last up to 37 hours and offer nine hours of continuous use per charge, far more than the AirPods 4 with ANC, which last five hours with ANC off and four with it on. A three-minute charge provides around an hour of playback. The app makes the sound heavily customizable, and while sound quality is robust and impressive, it’s not quite as bass-forward as in-ear buds.

Though they can’t overcome the limitations most open-ear designs face, the Sony LinkBuds Clip Open Earbuds are a reliable, long-lasting option for settings where you need situational awareness.

October Prime Day FAQs

How does Prime Day work?

Prime Day lets Prime Members shop online for thousands of products with big discounts. It only lasts two days, so make sure you check out everything we know about the sale before it starts.

Is Prime Day only for Prime Members?

Yes, you will need to be a Prime Member to shop the exclusive sales during Amazon's Prime Big Deal Days. Prime membership starts at $14.99 per month.

What goes on sale on Prime Day?

Since Prime Big Deal Days happens in the fall, you're likely to see more deals on gaming and indoor gym equipment. Amazon has already announced some of the 35 categories that will be on sale, including beauty, tech, kitchen, fashion, and home. Some brands Amazon has already mentioned are: Shark, Princess Polly, Soundcore by Anker, UGG, Nest New York, Sony, Tarte, Adidas, and Barefoot Dreams.

Our Best Editor-Vetted Tech Deals Right Now
Deals are selected by our commerce team

from Lifehacker https://ift.tt/eGNknmJ

CISA has added another Citrix NetScaler vulnerability to its Known Exploited Vulnerabilities catalog on Sunday: CVE-2026-88779, a memory overflow bug that may cripple vulnerable NetScaler ADCs and Gateways.

“Citrix has observed targeted attacks on unmitigated NetScaler deployments which can lead to Denial of Service. If the condition is triggered repeatedly, the service may remain unavailable,” the vendor stated.

“Our analysis indicates that this issue affects service availability, and we have not identified an impact on the integrity of customer data.”

Attacks observed after patching spree

Bishop Fox and watchTowr researchers have been credited with flagging CVE-2026-88779, and the latter have reproduced it, but have yet to share technical details.

Reddit users have been reporting that their organizations’ NetScaler appliances have been hit by crashes and reboots after they’ve upgraded to patch eight vulnerabilities, including two actively exploited zero-days: CVE-2026-88771 and CVE-2026-88772.

Apparently, the attackers are trying to exploit the flaw to download and run a script to install webshells.

Security researcher Kevin Beaumont reported attacks on his honeypots, from multiple IP addresses, and said he found a downloaded malware binary on one of them.

A threat hunter working at insurance company Geico has shared a SIGMA rule for identifying probing/scanning and exploitation attempts, but it’s still unclear if exploitation of this vulnerability can lead to successful remote code execution.

Affected versions and mitigation

The following supported NetScaler versions are affected by CVE-2026-88779:

  • Citrix NetScaler ADC and Citrix NetScaler Gateway 14.1 before 14.1-73.41
  • Citrix NetScaler ADC and Citrix NetScaler Gateway 13.1 before 13.1-64.28
  • Citrix NetScaler ADC FIPS before 14.1-73.41 FIPS
  • Citrix NetScaler ADC FIPS and NDcPP before 13.1-37.282

CVE-2026-88779 can be exploited on vulnerable on-prem NetScaler deployments only if the appliance has been configured to use SAML authentication (either as a service provider or an identity provider) in conjunction with Gateway or AAA functionality.

Citrix advised customers to upgrade to a fixed version and has pushed out signatures, usable via the Global Deny List feature, to reduce exposure while they plan the upgrade. The signatures should block access from known malicious IP addresses.

“Citrix provides an indicator of compromise script through NetScaler Console to check affected appliances for signs of compromise. Citrix notes that the latest script version can report a false positive about suspicious nobody processes even when it finds no compromise, so administrators should review results carefully and preserve evidence before applying the update,” watchTowr advised.

CISA has ordered US federal civilian agencies to address the vulnerability by October 7 and to check for compromise.

Subscribe to our breaking news e-mail alert to never miss out on the latest breaches, vulnerabilities and cybersecurity threats. Subscribe here!


from Help Net Security https://ift.tt/sPfFaUy

Your iPhone 18 Pro Max can do a lot. It has a variable aperture that lets you control the amount of light that hits the camera sensor; it can charge up to 50% of its battery in 15 minutes (with the right adapter, of course); and it can run all of Apple's latest AI features, thanks to the new A20 processor. But the 18 Pro Max is still, above all, a phone. If it can't connect to the cellular network, you no longer have an iPhone, but a glorified iPod touch.

Unfortunately, that's the situation some iPhone 18 Pro Max users find themselves in. Despite being "the best" iPhone Apple has ever made, Apple confirmed that a "small number" of 18 Pro Max units—specifically on the AT&T carrier network—can no longer connect to cellular service, with the devices only displaying an "SOS" icon at the top of their screens. That's a pretty glaring issue: Without cellular service, you'll need a wifi connection to use any apps or features that require the internet and you'll lose the ability to make calls over cellular entirely. It's so bad that some users may not even be able to call 911.

What if my iPhone 18 Pro Max can connect to cellular service right now?

If your iPhone 18 Pro Max has the ability to connect to cellular service, that doesn't mean you're in the clear. Just because there's nothing wrong with your unit yet, you can still be affected by the glitch, and you'll need to install the latest update, iOS 27.0.1, as well as the latest carrier update from AT&T, to ensure your 18 Pro Max won't be affected by these mysterious cellular issues in the future. That's what Apple told 9to5Mac in the following statement: “We have identified an issue affecting a small number of iPhone 18 Pro Max users on the AT&T network that may cause a device to lose service and be unable to make calls. We released iOS 27.0.1 earlier this week and strongly encourage all iPhone 18 Pro Max users to update now, and are also issuing a carrier settings update today. These updates together are meant to help prevent this issue from occurring.”

While you can always install iOS 27.0.1 from Settings > General> Software Update, Apple says that the carrier update will install on its own at some point over the next 14 days. However, I'd advise manually installing it by heading to Settings > General > About. There won't be any confirmation that the carrier update installs, but rest assured, this process will ensure that it has.

What if my iPhone 18 Pro Max cannot connect to cellular?

Unfortunately, if your iPhone is already experiencing issues connecting to cellular service, there is no fix. The updates above only help with prevention; they cannot patch an iPhone 18 Pro Max that already can't reach the network. Unfortunately, the only solution is to swap out the unit with either Apple or AT&T. The good news is your store will make the trade for you free of charge, as it is a hardware defect covered under warranty.

It's not clear why this issue is only affecting iPhone 18 Pro Maxes and not the standard iPhone 18 Pro, nor is it evident why only AT&T devices appear to be experiencing it. A possible point of failure: The iPhone 18 Pro Max uses a Qualcomm modem, while the iPhone 18 Pro uses Apple's proprietary C2 modem. Perhaps there's some flaw with Qualcomm's hardware specifically on the AT&T network.

That's not to say the launch of the iPhone 18 Pro has been otherwise drama-free—far from it. As it happens, the 18 Pro (along with the 18 Pro Max) has also experienced three other public-facing issues since Apple launched the devices last month. First, there was an issue with phones randomly rebooting following a failed Face ID attempt; next, some users noticed their devices emitting a cracking or popping sound through the speakers. Finally, some units also appear to be losing their exterior color. If you've upgraded, I hope your fancy new iPhone is doing well.


from Lifehacker https://ift.tt/IUjaPNQ

In this Help Net Security video, Drew McCombs, CTO and CISO at Cylerity, explains how he balances both roles. Security work is scheduled into every sprint, and issues touching patient data or funds disbursement come first.

He covers how Cylerity keeps PHI away from its bank partner, why AI models recommend but never act, and why turning on MFA for email is the cheapest fix for small practices. He also lists three questions a hospital CISO should ask a fintech vendor, and the answer that should end the talk.

healthcare fintech security

You hold both the CTO and CISO titles. When the roadmaps compete, who wins? How do you keep yourself honest?

I often find that these two roadmaps align well, and I don’t treat them as independent backlogs. Security is a core feature that is never complete, and it’s scheduled into every sprint so we keep making progress on key projects. It’s also discussed across the entire engineering team, which keeps it front of mind through all development instead of being something that comes after.

Additionally, our SDLC requires a full security scan of all development, and we keep investing in our foundation so we can deliver quickly without taking on new risk. This approach means most conflicts are handled before planning, and we have full visibility into our plan each sprint.

But when we have to choose, it’s clear: if an issue affects patient data or funds disbursement, it wins. Period. Beyond that, we balance feature delivery against steady progress on our core security initiatives.

Holding both titles does require visibility and accountability for progress on core security projects. That’s why they’re tracked and reviewed with leadership on a regular basis, so it’s clear what’s happening and when. That way, I’m not the only one making the call, and security is treated with the appropriate urgency.

Where do HIPAA and banking expectations contradict, and how do you resolve it?

It’s important to start with what Cylerity is and isn’t. Cylerity isn’t a bank and it does not factor receivables. We fund healthcare organizations using a bank credit facility, and we serve only businesses, not consumers. This means many of the core banking regulations don’t apply to us directly. Instead, the bank’s expectations reach us through our credit agreements and our partner bank’s diligence, which includes reviewing who our customers are, how funds are moved, what we report, and what they can audit.

That sits well with HIPAA, but the area that gets complicated is collateral. We lend against healthcare claims, and claims contain patient information (PHI). When the bank wants to discuss a customer’s borrowing base, it’s often helpful to get down to the line level, and that’s where we take a specific plan to make sure we’re not exposing PHI to the bank.

Here’s our approach. First, we always work with the minimum data required to support our customers. That usually means providing summarized information at the payer or customer level, with claim-level details removed. Second, if we need to get down to the line level, we don’t expose claim identifiers. We build our own unique identifiers for when we need that level of detail, so PHI stays protected. Finally, across the platform we keep PHI separate from the data needed for financing. That’s how we answer every data request, including our lending partners.

What’s the one control you’d insist on before a model touches money or patient data?

For me, it’s simple: the model doesn’t act. AI can recommend, summarize, or flag, but a person is always in the loop between its output and anything that releases funds or exposes patient data. We bring these insights into our underwriting and monitoring so our team has more information to make informed decisions, but the decision stays with our team.

Explainability is what makes that control work, but it isn’t the control itself. A reviewer can’t meaningfully approve something they don’t understand. So when a model surfaces a recommendation, it shows the source data it relied on, and our team checks against that source, not against the model’s own explanation. A model describing its own reasoning isn’t evidence.

The risk I watch most closely isn’t a dramatic attack. It’s gradual drift, where a reviewer approves the first hundred recommendations carefully and then starts rubber-stamping. We address that by involving multiple people in decisions and regularly reviewing decisions after they’re made.

What’s the most common weakness when onboarding a small practice, and the cheapest fix?

The most common weakness isn’t unique to small practices. It’s not unique to any business at all. MFA continues to be one of the most important controls, and it’s still underused. It’s especially important for the organizations we work with. They were built to deliver care and services, not to run IT, and many are handling patient data and healthcare payments for the first time.

That’s why the cheapest fix is also the most impactful: turn on MFA, starting with email. It’s usually already included in the email service they’re paying for. It’s table stakes, and closing that one gap shuts down the most common path to account takeover and payment fraud.

Our role goes beyond recommending it. Because we support our customers’ day-to-day revenue cycle, we see their claims and funding activity as it happens. That gives us the opportunity to spot activity that doesn’t fit their normal pattern faster than a small team could on its own. Additionally, when a deposit account change comes in, we confirm it by phone using a number already on file, never one provided in the request.

What three questions should a hospital CISO ask a fintech vendor, and which answer should make them walk away?

First, “Can you list every party that touches our data, including subprocessors, AI services, and any financing partners or their auditors?” If a vendor can’t produce that list quickly, they don’t know where your data goes. It’s important to remember that a fintech’s lenders may have audit rights over records that contain your patients’ information, and you should know that before you sign.

Second, “How do you verify a change to where funds are sent?” For a fintech vendor, payment redirection is the attack that costs real money. You want to hear about an out-of-band confirmation step that no one can skip, not “we review requests carefully.”

Finally, “Walk me through the first 24 hours after you discover a breach involving our data. Who calls whom?” You’re looking for names, roles, and timing, not a policy document. The answer that should end the conversation is “We’re HIPAA certified.” There’s no official HIPAA certification, so that answer tells you the vendor either misunderstands the rule or is counting on you not to know.

Webinar: Closing the accountability gap in AI-assisted delivery


from Help Net Security https://ift.tt/weQs0Dc

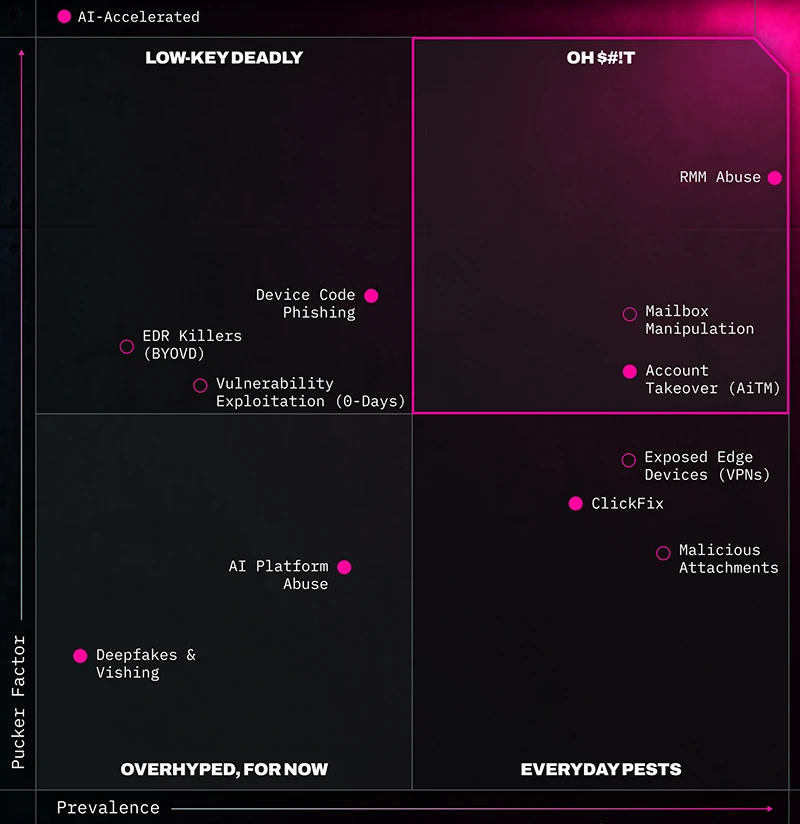
Huntress found attackers using legitimate remote monitoring and management (RMM) software in 45% of the endpoint-related incidents it recorded in the first quarter of 2026. The security company also ranked 11 attack tactics by how often it sees them and how much damage each can do, and RMM abuse sits farthest right on the chart, the position for tactics it sees most often.

RMM abuse

IT teams use RMM tools to manage computers from anywhere, so an attacker who installs one gets persistent access and remote command execution that looks like ordinary administrator work. Huntress calls the category one hop from ransomware or data theft and says it jumped 277% year over year in 2025. The malicious copy and the approved one can behave the same way.

One click, four tools

In one case, a fake service agreement installed an RMM tool called Tiflux, and the intruder then stacked UltraVNC, Splashtop, and ScreenConnect on the same device. One phishing click gave the attacker several ways back in. The researchers say attackers already use AI to write fake document-share and service-agreement lures.

“Why would you spend the cycles to develop or build from scratch when you can use a legitimate tool that you can just pull off the shelf?” said Jamie Levy, senior director of adversary tactics at Huntress.

The researchers suggests a quick check: ask the security team which RMM tools are approved and what tips them off when an unapproved one appears.

Hidden inbox rules and stolen session tokens

Huntress puts mailbox manipulation and account takeover in the same top-right corner. In mailbox manipulation, an attacker inside an inbox creates a rule that sends a vendor’s replies to a folder like Archive, where they are easy to miss, then swaps in an invoice that redirects payment. In adversary-in-the-middle (AiTM) takeovers, the attacker sits between a victim and the real Microsoft 365 login page and copies the session token, the credential that keeps a user signed in. While that session stays valid, the attacker needs no password and triggers no MFA prompt.

Mailbox manipulation made up 19% of identity-based threats in 2025 and 24.6% of identity threat signals so far in 2026. AiTM was 18.9% of identity-based threats in 2025. Those figures count different things than the 45% for RMM, which counts endpoint-related incidents, so they cannot be ranked against it. The researchers suggest asking IT how long sessions stay active and whether a new device or location forces a fresh login.

Fake codes, fake CAPTCHAs, a fake Claude download

Device code phishing sits in the “low-key deadly” corner, which Huntress reserves for tactics it sees less often but that do heavy damage. A fake workflow prompt sends someone to Microsoft’s real device code login, and once the victim enters the code, the attacker holds an access token that can survive a password reset. The researchers report a 1,380% increase year over year, but the periods compared are July through December 2025 and January through April 2026, and no starting count is given. The figure shows direction; with no base, it cannot show volume. The EvilTokens phishing kit hit 344 organizations across five countries in 16 days.

ClickFix made up 53.2% of malware loader activity in 2025. Huntress files AI platform abuse and deepfakes under “overhyped, for now.” One AI platform case: FakeAgent used a malicious Claude Artifact hosted on the real claude.ai domain to send people looking for Claude Desktop to SectopRAT, hitting 29 organizations in two days. Six of the 11 tactics carry Huntress’s marker for AI acceleration, including both of those.

Webinar: Closing the accountability gap in AI-assisted delivery


from Help Net Security https://ift.tt/GC7fMNW